If you operate a WooCommerce store in high Cash-on-Delivery (COD) markets—such as South Asia (Bangladesh, India, Pakistan), MENA (UAE, Saudi Arabia, Egypt), or Eastern Europe—your biggest profit killer isn’t rising ad CPMs.
It is Return-to-Origin (RTO) courier losses and fake COD orders.
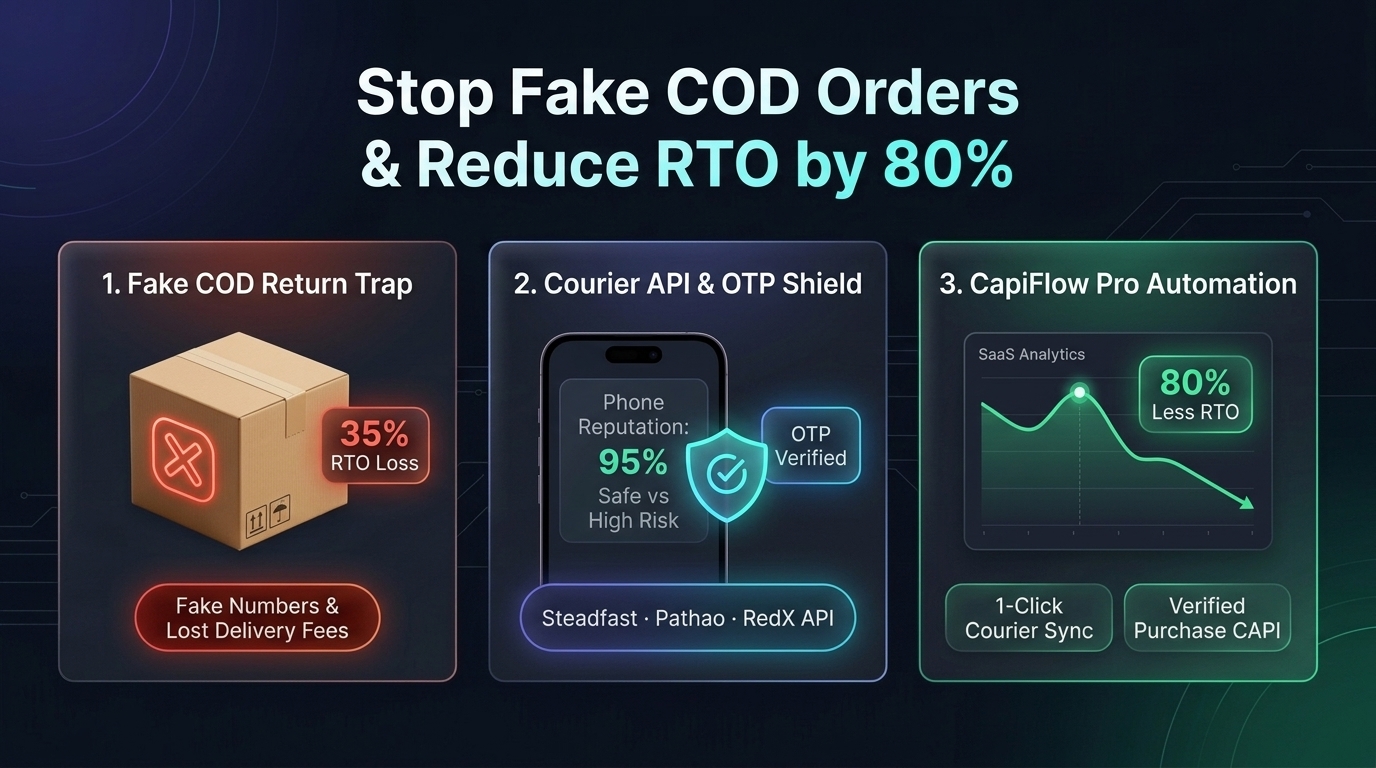
When 25% to 35% of your dispatched parcels are rejected at the doorstep because of fake phone numbers, prank orders, competitor sabotage, or impulsive buyers refusing delivery, your business suffers a devastating double blow:
1. Direct Logistics Bleed: You pay two-way forward and return shipping charges, packaging costs, and inventory lockup on every uncollected parcel.
2. Meta Pixel Poisoning: Standard tracking plugins fire a Purchase event to Meta the instant the fake order is submitted at checkout—training Meta’s Advantage+ AI to spend your remaining ad budget finding more fake COD buyers.
In this engineering guide, we walk through the 5-layer WooCommerce COD Fraud Prevention Architecture that reduces courier RTO from 30% down to under 6%.
💡 Want an all-in-one automated solution? Explore our WooCommerce COD Fraud Prevention Shield and Courier Webhook Automation Engine.
1. Screen Customer Courier Delivery History Before Confirming Checkout
Most WooCommerce merchants only discover a buyer is a serial returner after the parcel has already been packed, booked with the courier, and rejected at the customer’s doorstep.
The Technical Solution: Real-Time Courier Success Scoring
When a customer enters their mobile number on your WooCommerce checkout form, your backend should query aggregated courier delivery databases (Steadfast, Pathao, Redx, and historical WooCommerce order records) in real time:
Green Tier (85% – 100% Delivery Success Rate): Verified high-trust buyer. Approve COD and push to 1-click courier booking immediately.
Yellow Tier (60% – 84% Delivery Success Rate): Moderate risk. Require automated SMS OTP verification or confirmation call before dispatch.
Red Tier (<50% Delivery Success Rate or Serial Returner): High-risk profile. Automatically hide Cash on Delivery on the checkout page or require an upfront shipping fee deposit via digital payment (bKash, Nagad, SSLCommerz, or Stripe).
2. Enforce Strict Phone Regex Validation & Disposable Input Blocking
Out of the box, WooCommerce’s billing phone field accepts almost any string of digits—allowing bots and pranksters to submit 01700000000, 1234567890, or incomplete addresses.
Mandatory Checkout Guardrails:
1. Operator Prefix & Length Regex: Validate exact telecom operator prefixes (e.g., 11-digit BD mobile format ^01[3-9]d{8}$ or international E.164 format) before the checkout form can submit.
2. Repetitive & Sequential Digit Blocker: Automatically reject bogus sequences like 01711111111 or 01712345678.
3. Cooldown & Velocity Limiting: Block repeat orders from the same phone number, IP address, or browser fingerprint within a configurable 24-hour window if a pending order already exists.
3. Stop Firing Instant Meta Purchase Events on Unverified COD Orders
This is the single biggest blind spot for 95% of e-commerce media buyers.
Standard plugins (like PixelYourSite or cloud containers like Stape.io) fire the Meta Purchase event the second the WooCommerce /order-received/ thank-you page loads.
Why This Destroys Your Ad Account:
A prankster or competitor submits a $150 COD order with fake details.
Your browser pixel tells Meta: “We just acquired a high-value $150 buyer!”
Meta’s machine learning algorithm builds lookalike audience clusters around that fraudster’s behavioral profile and floods your store with low-quality traffic.
4. Connect Courier Delivery Webhooks to Meta Graph API v26.0
To keep your Meta Pixel 100% clean while retaining full attribution accuracy, your store must use a Verified Purchase Event Pipeline:
1. Hold at Checkout: When a COD order is placed in Pending or Processing status, CapiFlow Pro captures and stores the buyer’s 180-day persistent server cookies (_fbp, _fbc), client IP, user-agent, and SHA-256 hashed PII in WooCommerce HPOS order meta—without firing the Purchase event prematurely.
2. Courier Webhook Trigger: When Steadfast, Pathao, or Redx confirms physical parcel handover (Delivered / Completed), CapiFlow Pro automatically dispatches the verified server-side Purchase event via Meta Graph API v26.0 using the original checkout session identifiers.
3. Negative Purchase on Cancellation: If the order is cancelled or returned (Cancelled / Refunded), CapiFlow Pro sends a NegativePurchase signal so Meta’s AI actively excludes chronic returners from your ad targeting.
5. Pre-Submit Checkout Capture for Abandoned Orders
What about real customers who enter their phone number at checkout but close the tab before clicking “Place Order” due to network drops or delivery fee hesitation?
CapiFlow Pro includes Zero-Latency Pre-Submit Cart Abandonment Capture:
As soon as a shopper types a valid phone number or email on the checkout form, it is asynchronously saved to your recovery queue.
If they do not complete the order within 15 minutes, your team can follow up via WhatsApp, SMS, or call to recover 15%–25% of lost revenue.
Summary Comparison: Standard WooCommerce vs CapiFlow Pro
| Protection Layer | Standard WooCommerce Setup | CapiFlow Pro COD Shield |
|---|---|---|
| Phone Format Validation | Accepts any random digits | Strict telecom regex & repetitive digit blocker |
| Courier Fraud Screening | Discovered after parcel return | Live Steadfast, Pathao & Redx success ratio at checkout |
| Repeat Prank Orders | Unlimited duplicate submissions | IP, device fingerprint & phone cooldown lock |
Meta CAPI Purchase Logic |
Fires instantly on fake orders | Fires via Graph API v26.0 only on verified delivery |
| Average Courier RTO Rate | 25% – 40% | 5% – 8% |
Ready to eliminate fake COD orders and train your Meta Pixel on 100% real buyers?
Explore WooCommerce COD Fraud Prevention → | Get CapiFlow Pro Today →